

Forge has no organization-level secrets. Organization admins can list the names of members’ personal secrets, but never their values, and can delete them. On Dedicated Cloud and Self-Managed, organization admins can also create members’ personal secrets and replace their values. Admins manage members’ secrets through the API. User settings show only your own personal secrets.
After you save a secret, neither the UI nor the API shows its value again. You can see a secret’s name and when it was last updated, but not its value. To change a value, replace the secret.
How Forge chooses between a personal and a team secret
Forge features find a secret by its name. For example, W&B Weave Playground looks forOPENAI_API_KEY to call OpenAI models. To make a credential available to a feature, store it under the name that feature expects.
A personal secret and a team secret can have the same name. When a feature looks up a secret on your behalf in a team’s project, it resolves the name in this order:
- Your personal secret with that name, in the organization the team belongs to. A team belongs to exactly one organization.
- The team secret with that name, if you don’t have a personal secret with that name.
Where personal secrets apply
Personal secrets apply wherever a feature looks up a secret on your behalf in a team’s project. This includes:- Weave: Playground, the project’s AI Providers tab, custom runtimes, evaluations, and scorers, including remote scorers.
- Sandboxes on serverless capacity: The sandbox resolves secrets for the user who owns the API key that created it.
- Webhook automations: A webhook uses only the team secrets you select when you configure it.
- Work without a user: Work that runs as a service account, such as a monitor that a service account saved, has no user whose personal secrets Forge can use. Remote scorers and LLM judge scorers in such a monitor use team secrets instead. An LLM judge scorer that uses a W&B Inference model fails in such a monitor.
WANDB_API_KEY: Weave never resolvesWANDB_API_KEYfrom a personal secret.
Availability
- Multi-tenant Cloud
- Dedicated Cloud and Self-Managed
Personal and team secrets are available by default.You can belong to more than one organization, and your personal secrets are scoped to one organization each. A personal secret in one organization isn’t available in another, and you can create personal secrets with the same name in different organizations.
Manage personal secrets
Manage your personal secrets in the Personal secrets section of your user settings. To open the section:- Click the account selector in the upper-right corner.
- Select User settings.
- Scroll to Personal secrets.
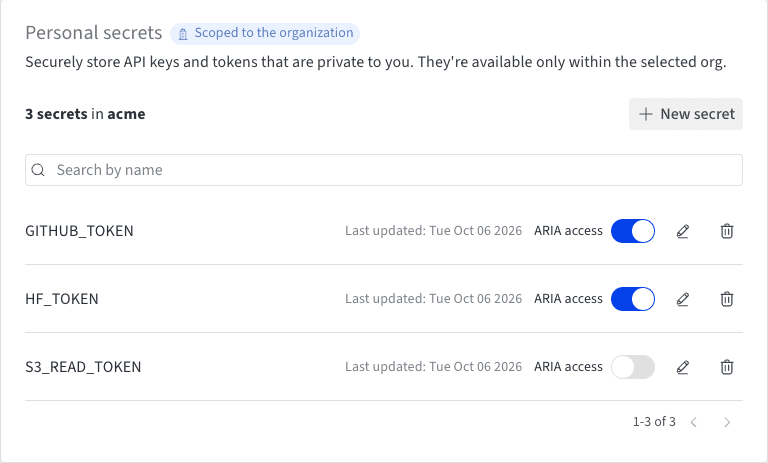
Create a personal secret
To create a personal secret:- In the Personal secrets section, click New secret. If you don’t have any personal secrets yet, click Create new secret instead.
-
Enter a Name for the secret, in environment variable form: letters, digits, and underscores (
_), not starting with a digit. For example,GITHUB_TOKEN. You can’t reuse the name of another of your personal secrets in the same organization. If a team secret with the same name exists, the drawer shows A team secret with this name exists and lists the teams, but lets you save. Your personal secret then takes precedence over the team secret for you. - Paste the sensitive value into the Value field. To check what you pasted, click Reveal secret value. To hide it again, click Hide secret value.
- On Multi-tenant Cloud, the drawer also includes Allow ARIA to use this secret, which is on by default. To store the secret without granting ARIA access, turn it off.
- Click Save secret.
Replace the value of a personal secret
To replace a personal secret’s value, such as when you rotate a token:- In the secret’s row, click Edit secret (the pencil icon).
- Paste the New value. You can’t change the secret’s name.
- Click Replace secret.
Delete a personal secret
Deleting a personal secret is permanent, whether you delete it or an organization admin does. Features that support personal secrets fall back to a team secret with the same name, if one exists, or stop working if none does. ARIA loses access to the secret. To delete a personal secret:- In the secret’s row, click Delete secret (the trash icon).
- In Enter the secret name to confirm, type the secret’s name.
- Click Delete.
Manage team secrets
Team secrets live in each Forge team’s Secret Manager, in the Team secrets section of the team settings. Only team admins can create, edit, or delete a team secret, and the Team secrets section appears only if you have permission to edit team settings.Add a secret
Add a team secret when you want to make a sensitive value available to the whole team without exposing it in code or configuration. After you complete these steps, the secret is available by name to the Weave and Sandboxes features listed in Where personal secrets apply, and to webhook automations that you configure to use it. To add a team secret:- If an external service gives you a token or API key, obtain that value through that service’s normal flow. If necessary, save the sensitive string securely, such as in a password manager, before you paste it into Secret Manager. Forge doesn’t reveal the secret’s value after creation.
- Sign in to Forge and go to the team’s Settings page.
- In the Team secrets section, click New secret.
- Provide a name for the secret, using letters, digits, and underscores (
_). The name must start with a letter or an underscore. - Paste the sensitive string into the Value field.
- Click Add secret.
After you configure a secret in a webhook, you can access that secret in the automation’s payload using the format
${SECRET_NAME}.Rotate a secret
Rotate a team secret when its value changes, for example, when an upstream credential is regenerated or when you suspect the existing value has been compromised. Because Forge doesn’t reveal a secret’s current value after creation, rotation is also the way to replace a value you no longer have a copy of. To rotate a team secret and update its value:- To open the secret’s details, click the pencil icon in the secret’s row.
- Set New value to the new value. Optionally, click Reveal secret value to verify the new value.
- Click Replace secret.
Delete a secret
Delete a team secret when no team feature uses it. Because deletion is immediate and permanent, confirm that no automations, sandboxes, Playground providers, or other consumers still reference the secret before you proceed. Deleting a team secret affects every provider that uses it. To delete a team secret:- In the secret’s row, click the trash icon.
- Read the confirmation dialog, then click Delete.